WordPress malware removal & security auditing
If your WordPress website is showing signs that it may have been compromised, or Google Search Console is flagging pages as hacked, your site may have been infected with malware which could be leaking customer data.
Is your WordPress website showing signs of being compromised?
You may not even realise your WordPress website has been compromised. However, if your website is showing signs such as:
- Pages randomly redirecting to third parties or to spam sites
- Google showing a “This site may be hacked” warning
- Unfamiliar or spam pages showing in Search Console indexed/non-indexed pages list
- E-mails from your domain landing in other people’s spam folders
…it’s possible your website has WordPress malware, or a code “virus” somewhere in the theme, plugins or core files.
What should you do next if your website is showing signs of being compromised?
If your website is showing signs of being compromised – especially if you collect customer data e.g. through e-commerce purchases, contact forms, etc – we strongly advise you put it into maintenance mode as a first step. This won’t stop the malware but it prevents any further customers or users from submitting data which may end up revealed to malicious third parties.
After that, you should reach out to a specialist WordPress malware removal company or WordPress security specialist for a malware audit. Ultimately Better malware auditing starts at £400 + VAT.
UK Cybersecurity Specialist
Ultimately Better’s malware auditing, website clean-up and security testing services are led by experienced UK cybersecurity professional Jem Turner.
With over 20 years of experience working with WordPress and notable mentions in industry publications for her independent security research, Jem has seen it all when it comes to WordPress malware.
Watch Jem Turner on Wordfence podcast Think Like a Hacker, episode 35.
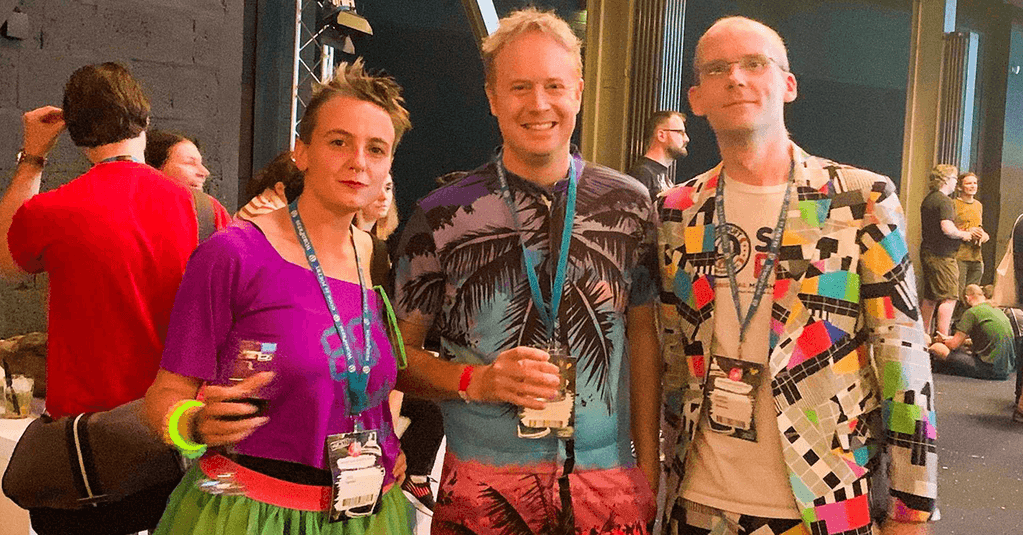
Pictured: Jem Turner (left), Mark Maunder, CEO of WordPress security company Wordfence (middle), and Gareth Griffiths (right)
What our clients say
Jem leads this business with timely, straight forward language, and practical measures. Her handling of the recent cyber security situation has been brilliant .
Jo Umbers, Managing Director Bladder & Bowel
Malware auditing and site clean-up process
Step 1: the malware auditing process
Before we remove any malware, we need to know what we’re dealing with. Not only to ensure we remove every trace of the malicious code, but to ensure we have a full log of what happened for reporting purposes. This process involves:
- Downloading a full backup copy of your website, so that we can work in a sandboxed environment
- Downloading log files to look for suspicious patterns of behaviour to help identify the vulnerability that was exploited
- File integrity checks for WordPress plugins and core files
- Database checks to look for injected scripts, rogue users, autoloaded options that shouldn’t be there
- Server environment checks to scan for unwanted additions to server config files and auto-reinfecting cron jobs
Once we’ve completed this process, we prepare an audit report on the scope of damage done and any risks, including recommendations on next steps e.g. whether or not you need to report the breach to the Information Commissioner’s Office (ICO) as per the UK GDPR legislation.*
* A reportable breach must be declared within 72 hours of you becoming aware of it.
Step 2: the clean-up process
Our audit report also contains a list of next steps and costed clean-up work needed to bring the site up to ‘safe’ standards again. If you choose to proceed with the clean-up work with us, this generally involves:
- Backdoor removal – we stop the bad actors from gaining re-entry by removing backdoors from the code, database, other files
- We replace WordPress core and all plugins and commercial (non-custom) themes with fresh guaranteed ‘clean’ copies, and perform manual clean-up on any bespoke themes or plugins
- Full database clean-up, removing any injected scripts, spam content, rogue user accounts and so on
- We perform credential resets across the server, FTP, database, WordPress admin accounts, etc as well as advising on any API key cycling as necessary
- If Google has flagged your site as having malware, we can help or advise on how to submit a review request in Google Search Console
Step 3: post clean-up and ongoing
Once your site is clean, it’s crucial that it’s actively maintained to prevent it from being reinfected. We will advise on how to keep the site safe going forwards, including advising and costing:
- Ongoing maintenance services
- Security hardening such as 2FA for admin accounts and shop managers
- Firewall configuration improvements or integration with Cloudflare
- Regular penetration testing
What our clients say
Great support for our website from Jem and the team. Always quick to respond and good at finding practical solutions without breaking the bank.
James Sales, In The Saddle Limited
Why choose us?
What’s so great about Ultimately Better anyway?

Real developers, not tinkerers
At Ultimately Better, our developers undergo a rigorous vetting process to ensure that they can actually write code, and that it meets internal and WordPress best practices

Honest assessments
Our WordPress audits are honest and backed by facts. We’ll tell you where things are going wrong, why, and what (if any) risks those problems pose.

No contract lock-in
Decide we’re not for you? You’re free to go at any time, with no fixed terms or contract lock-in. WordPress empowers ownership and we reflect that in our approach.

Great customer service
Customer service is at the heart of everything we do, and we have our customer commitment to prove it.
What our clients say
Swift resolution of a ‘critical error on website’ issue.
Ivor Chapman, hobby website owner
Helped get my website up and running and operating better than before.
Would recommend their services, especially for anyone who is anxious about doing the “nuts and bolts” themselves.
Frequently asked questions
How do I know if my WordPress site has been hacked?
Sometimes it’s obvious – you see keyword spam in your blog posts, or pop-ups that weren’t there before – but sometimes it’s not. Some of the signs may include:
- Visitors are redirected off site to gambling or ‘pharma’ pages
- Google shows warnings when trying to click through to your site from its search engine results pages
- Unfamiliar pages appear in Google’s results for your site or brand search terms
- Your host has suspended your account for suspected malware, or your host’s firewall has flagged suspicious code
- There are admin users in your dashboard that nobody recognises
- The site has become much slower all of a sudden and it’s not obvious why
If you’re unsure about whether or not your WordPress site has been compromised we can take a look. If there’s no sign of malware, you won’t be charged the full audit price. Reach out to discuss in more detail.
What do I get in my malware audit? Is clean-up included?
The malware audit covers discovery and record taking, clean-up costs are extra and depend on the scope of the infection and what work needs performing to make the website safe again.
How quickly can you perform a security audit on my WordPress website?
We treat compromised websites as an emergency and fit them in within 24hrs of the audit invoice being paid. We can sometimes offer an expedited service for additional fees, ask us if you need this service.
Google is showing warnings about my WordPress site, does that mean it’s infected?
It depends on the warning. If Google is showing “this site may be hacked” under your search listing, or an in-browser warning such as “deceptive site ahead”, this means that yes, Google has detected something harmful on your site. This isn’t always your website infected, sometimes it means you’re loading a compromised third party script, but either way it needs investigating.
You can usually see what Google has found using Google Search Console. Provide this information to us when reporting the problem as it helps speed up discovery.
How long does malware auditing and website clean-up take?
Full malware auditing usually takes around half a day, sometimes longer for larger sites such as e-commerce stores. Clean-up depends on the scope of the infection and how much remedial work is involved.
Do I need to tell my customers that my website has been hacked?
Sometimes, yes.
If no personal data was breached, e.g. your website doesn’t store contact form data within the website or you don’t have accounts and orders, you are less likely have a legal obligation to inform anyone.
However, if any personal data (customer names, e-mail addresses, order details, healthcare data) was involved, regardless of whether or not it was unlikely to have been touched, UK GDPR regulations kick in.
If card details may have been taken, e.g. through malware like card skimming on a WooCommerce checkout, you should also contact your payment provider straight away.
If you’re worried that your customers data may have been exposed, contact us as soon as possible. The ICO 72-hour reporting window starts as soon as you become aware of the breach, not when the clean-up is complete.
Is WordPress less secure than other platforms?
No. WordPress has a dedicated core security team that find, fix and roll out updates automatically. Further, because the core code is open source and viewable by everyone, more people outside of the core team can find and report vulnerabilities more often/more quickly. Serious vulnerabilities within the WordPress core software are rare.
However, WordPress sites do get compromised more often than sites on other platforms, for other reasons:
- WordPress is the most popular content management system in the world. That makes it the biggest target, so is statistically more likely to receive attempted attacks.
- As mentioned above, the code being open source means more people to find security bugs and report them to the right channels (great!) but also means more nefarious eyes who are up to no good and use the discoveries for their own gain.
- Any developer can publish a theme or plugin – even more evident with “vibe coding” becoming popular – and those themes and plugins end up on WordPress websites without any sort of security review process, opening holes in the process.
Hosted platforms such as Shopify or Squarespace handle security for you, but the trade-off is less control over how your site works and where that data is stored. They’re also not completely insusceptible to breaches of their own.
A WordPress site that is kept up to date, with sensible precautions and hardening through additional measures such as two-factor authentication on admin accounts is no less secure than any other website.
Should I move off WordPress because of recent high-profile hacks?
No, we don’t recommend moving off WordPress just because a particular hack or breach makes the news. The more useful questions to ask are:
- Is my site and its plugins up to date?
- Have I installed a plugin or theme from an unknown source that needs independently checking?
- Have I recently reviewed my list of admin users to make sure any redundant or legacy accounts are removed?
- Has anyone checked the data retention policies to ensure we’re not keeping data indefinitely which increases customer risk in the event of an attack?
There are good reasons to move off WordPress for some types of user and some types of website, but a high profile website breach isn’t one of them. If you’re worried about whether a recent incident affects your site, get in touch and we’ll check for you.